2026 Lending Hacks: 7 in 10 Protocols Had Been Live Over a Year
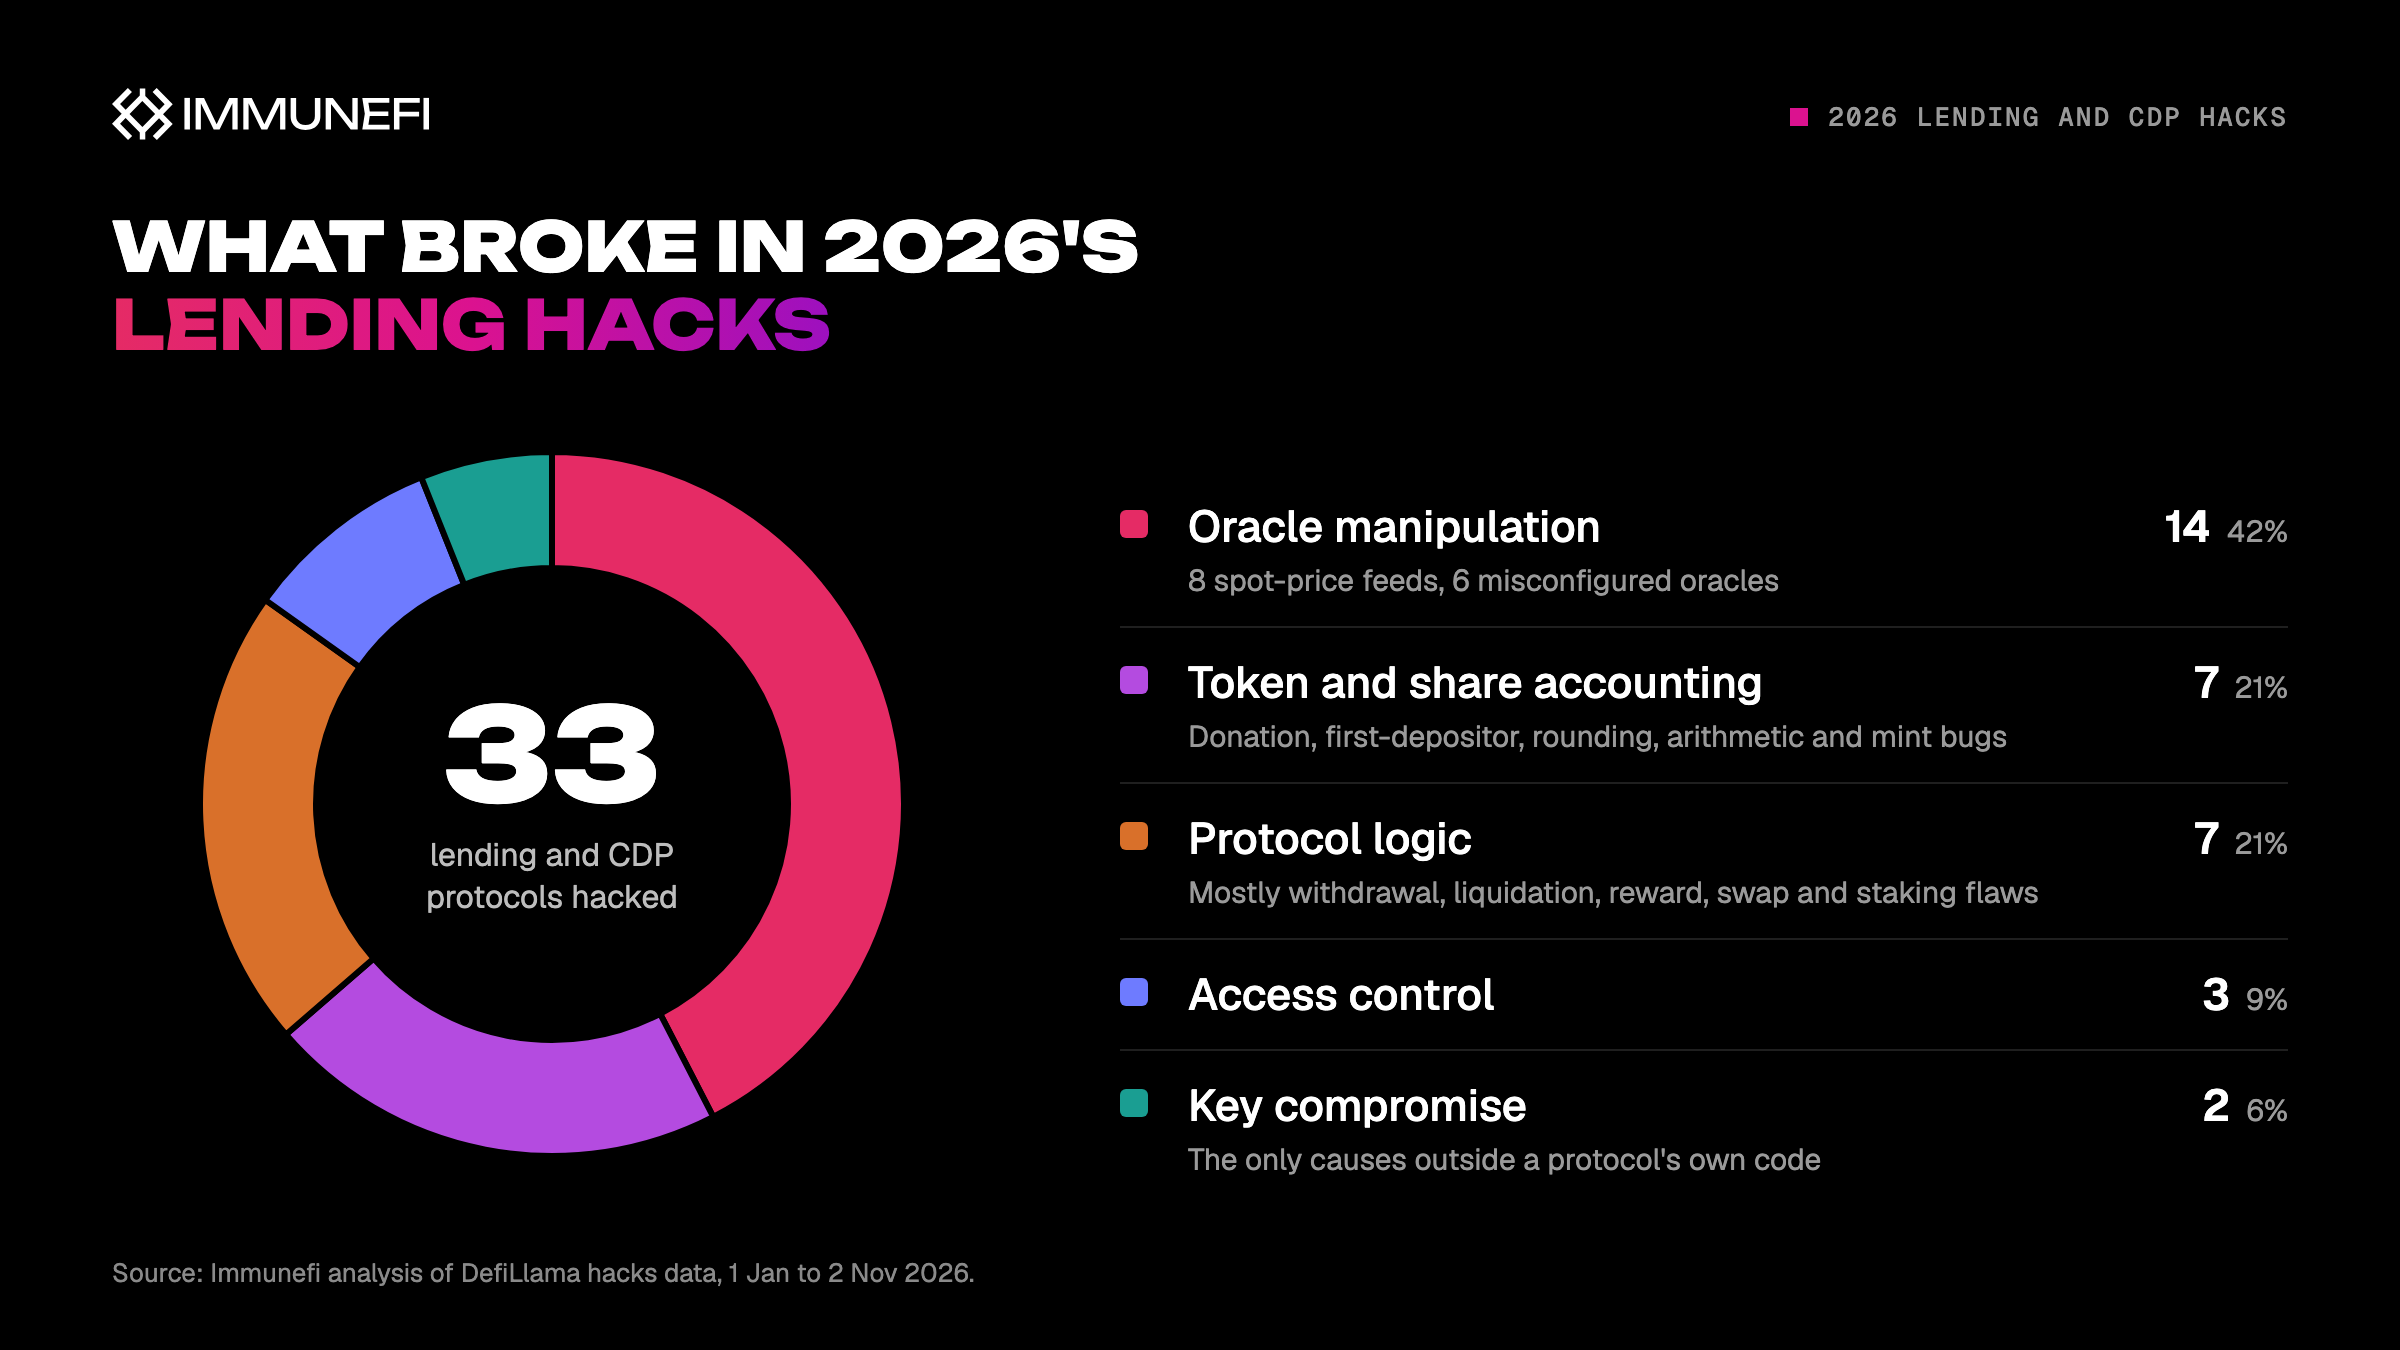
At least 33 lending and Collateralized Debt Position (CDP) protocols were hacked this year. Data shows attackers target protocols of all sizes, and vulnerabilities can still be found years after code was published.

Common wisdom leads users to believe small protocols will stay under the radar and that code that has withstood the test of time can be trusted. That was a valid assumption while the cost of an attack was measured in hours of human labor, but now it is measured in AI tokens.
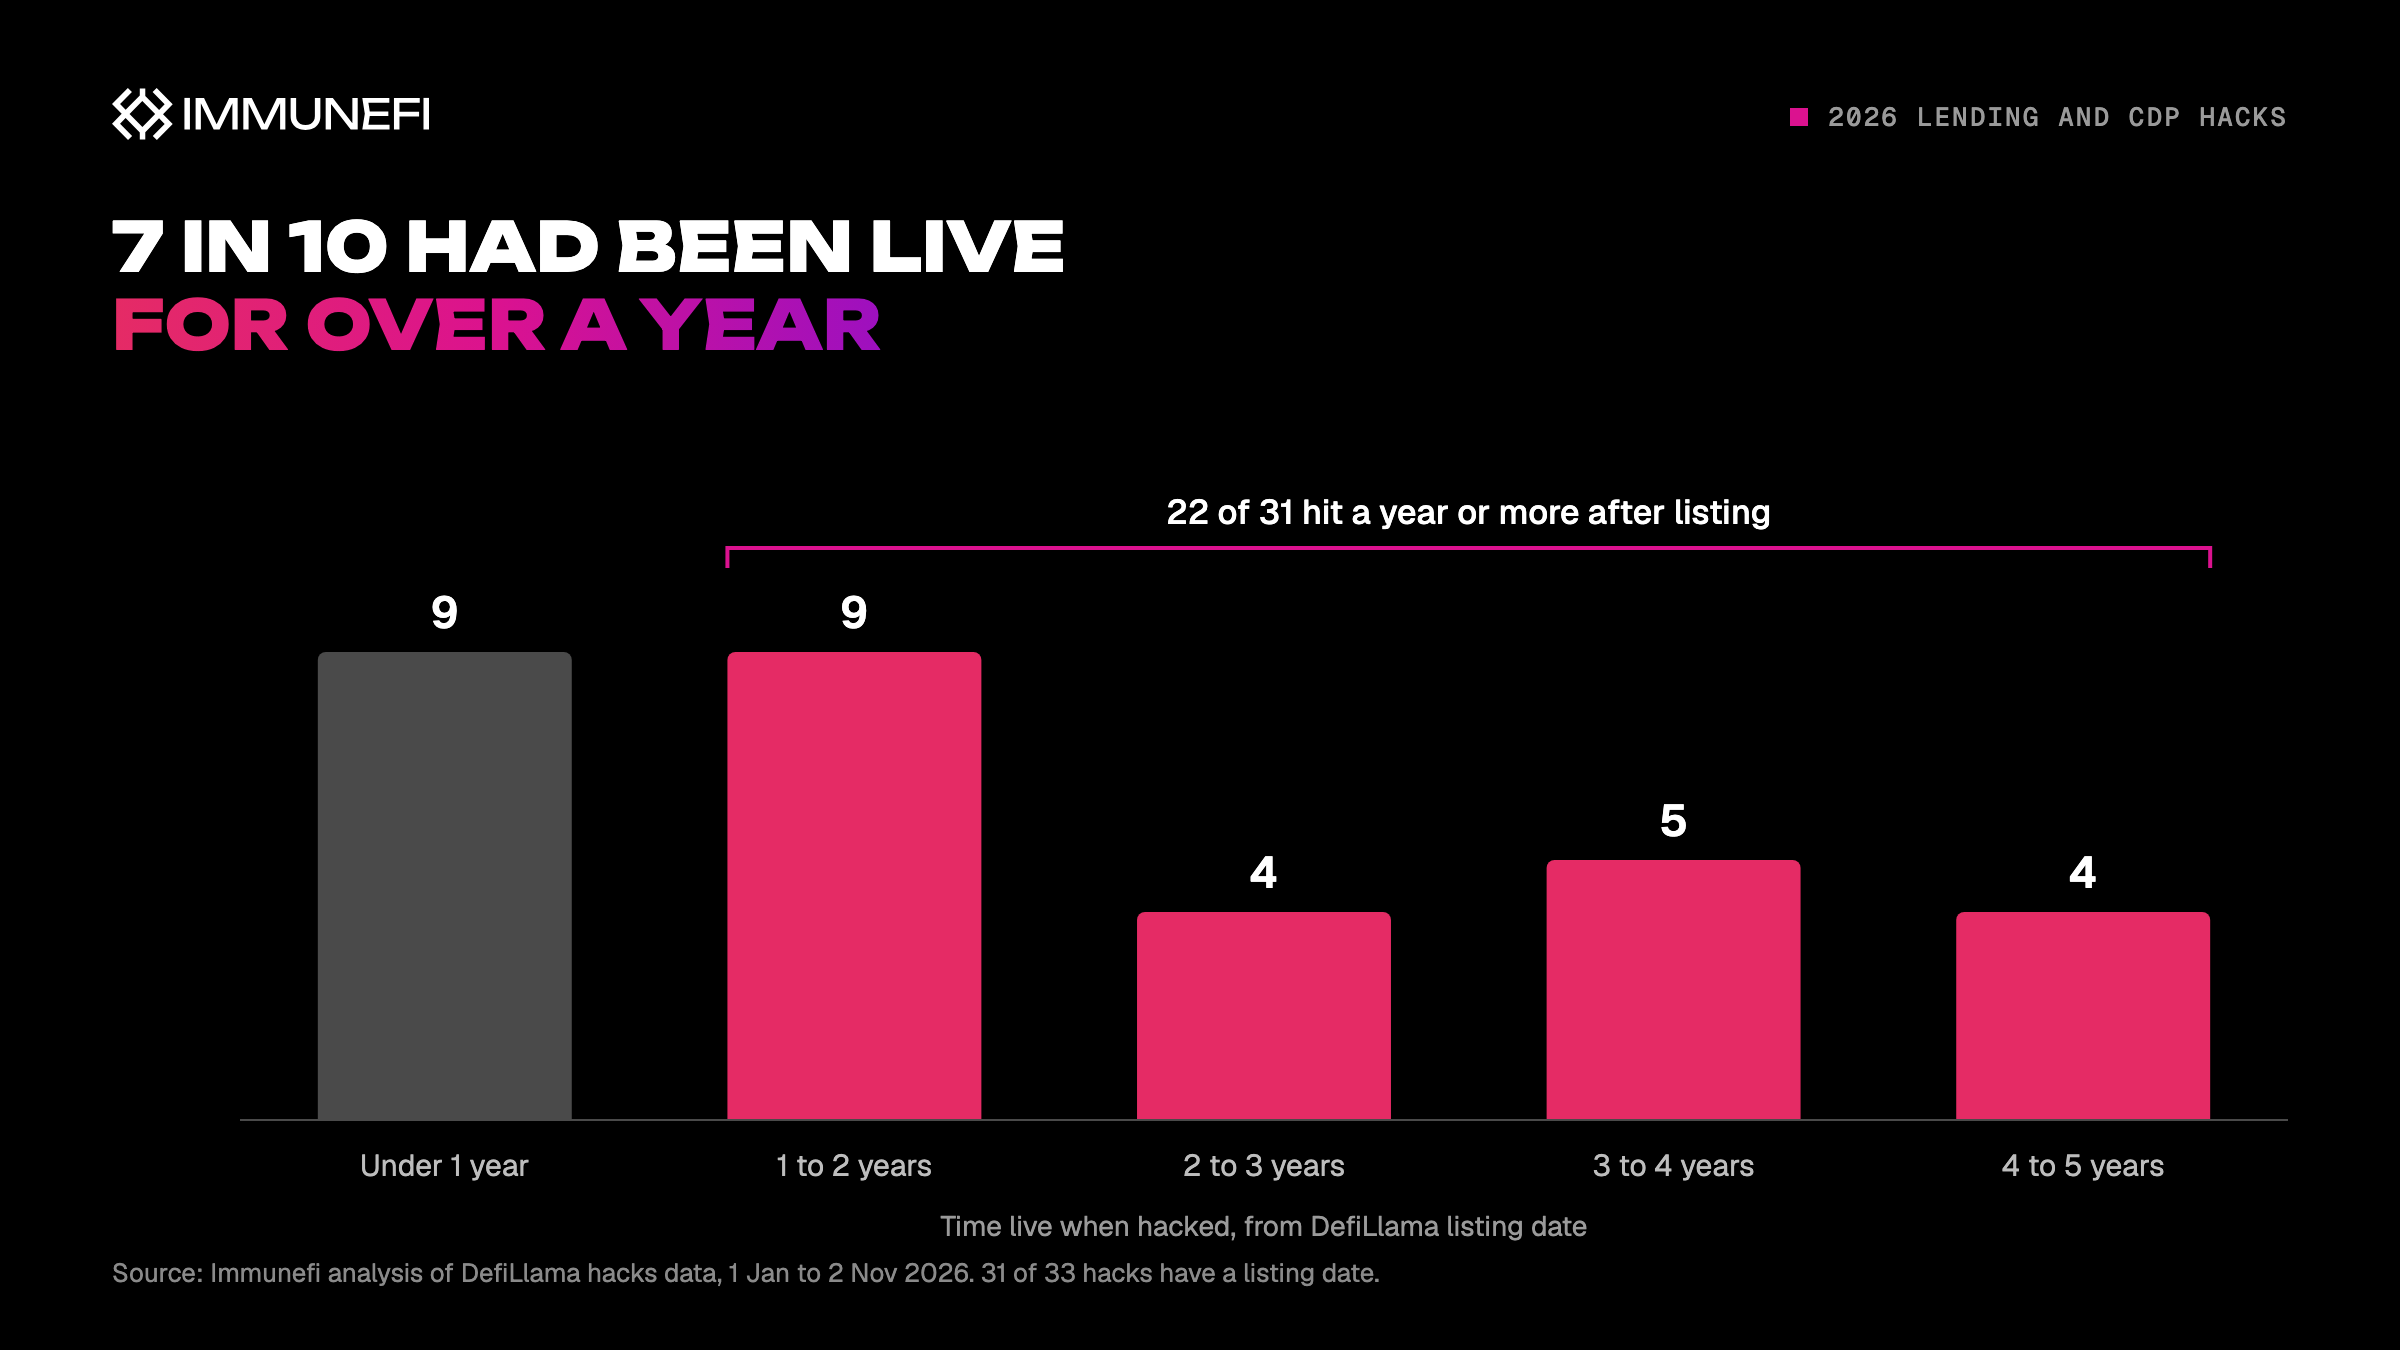
As of November 2nd, at least 33 lending and CDP protocols have been hacked in 2026, with a median loss of $756,000. Of the 31 with a DefiLlama listing date, 22 had been listed for a year or more when they were hit. Attackers are spreading out, and smaller protocols are now in range, no matter how old they are.
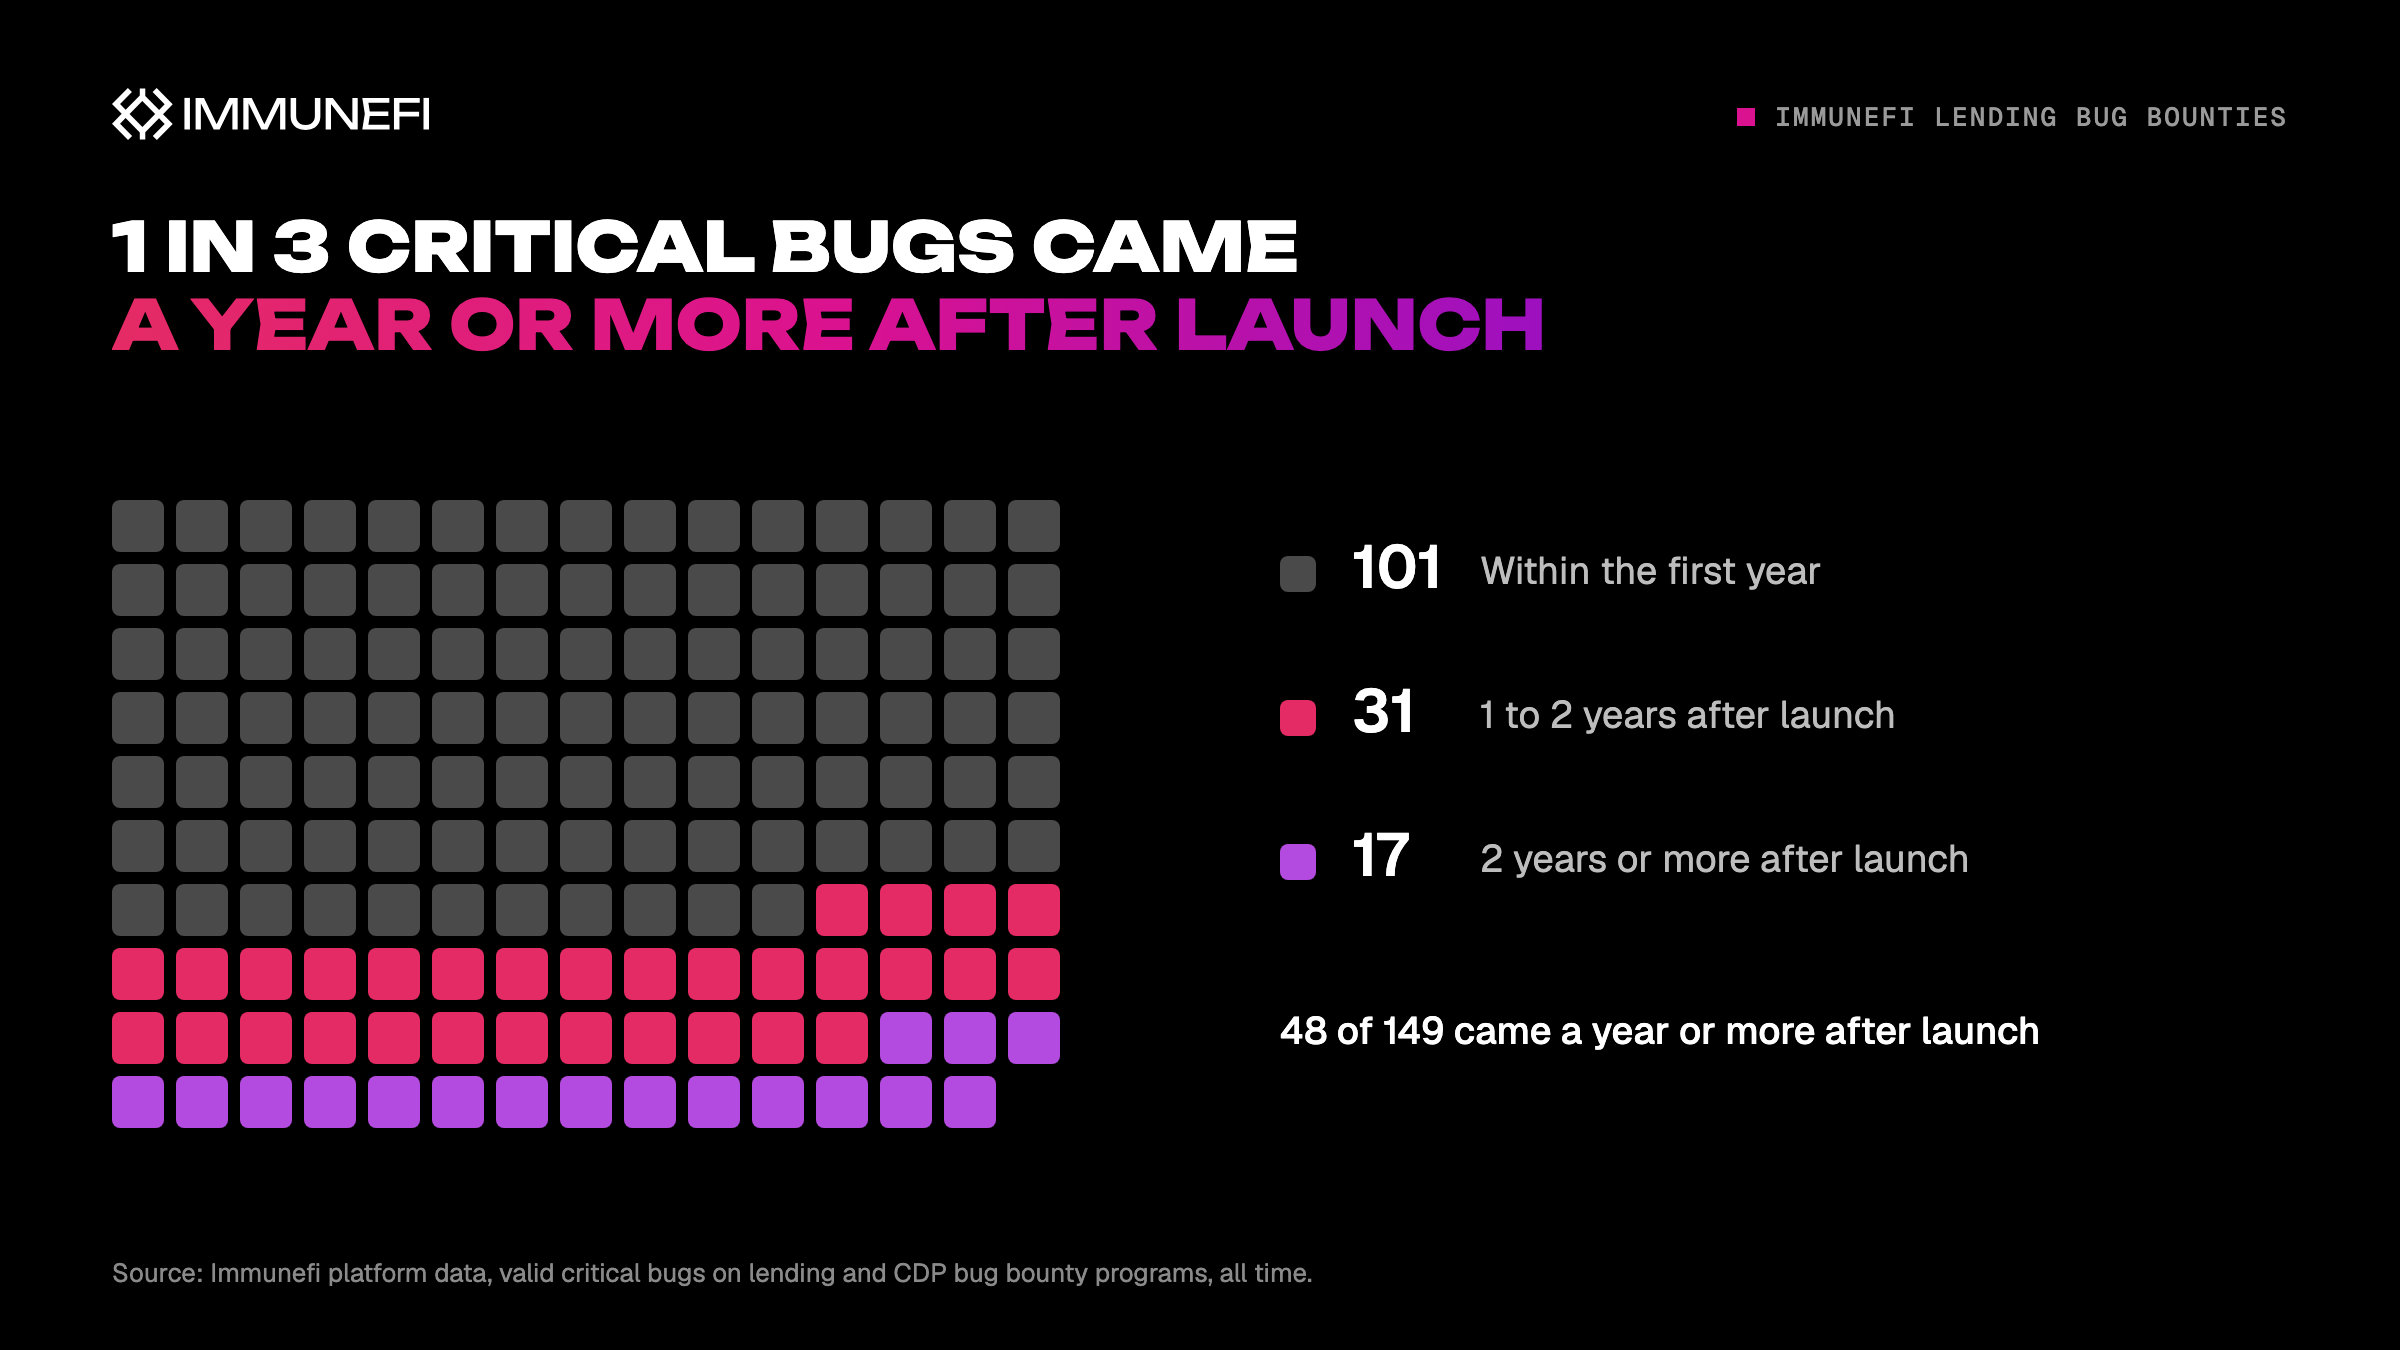
Lending bug bounty programs on Immunefi show bugs keep turning up in old code: 1 in 3 of 149 confirmed critical bugs came a year or more after the program went live. As long as there are deposits, code stays a target. No number of audits can make code bulletproof, but motivated researchers can find vulnerabilities before attackers do.
The critical bug that got past five reviews
Alchemix, the self-repaying loans protocol, relaunched as V3 in April 2026 after five security reviews. Just two months later, a researcher reported a critical bug in one of V3's vault strategies through Alchemix's bug bounty on Immunefi. About three hours later, Immunefi had triaged the report and escalated it to the team. They fixed it before any funds were lost.
Alchemix could act quickly because it runs the highest tier of Immunefi’s Managed Triage. In the 12 months to October 2026, our triage closed 89% of reports sent to the team, so its engineers saw only the submissions that needed attention.
The five pre-launch reviews, one of them an Immunefi audit competition, found 17 bugs rated critical, but the flaw that survived into production was found by an independent researcher incentivized by the bounty program. Alchemix paid the researcher nearly $300,000, the program's top reward at the time. According to DefiLlama, the protocol held over $30M in its smart contracts as of June.
"...their triaging services have saved us hundreds of hours... Immunefi helps keep the signal high and noise low." Alchemix team
A record year for exploits
Across all of crypto, DefiLlama has recorded $8.78B lost in 328 hacks in 2026 as of early November, the most for any year in its records. Although the top 5 hacks account for over 85% of the losses, with $6.36B from Binance alone, the number of hacks has increased 2.7 times from 2025, and the median loss has dropped from $1.07M to $0.51M.
Lending protocols show the same pattern. 33 were hit for a combined $192M in 2026. One incident accounts for about two-thirds of that, and of the other 32, 22 lost less than $1M. These amounts rarely make headlines, but show attackers are going after targets both large and small.
Old protocols are being targeted as much as new ones, and code that has been in production for a long time may still be at risk.
What a lending team can run
Three things keep a lending protocol covered after launch:
- A bug bounty on live code. It keeps researchers reading your contracts for as long as they hold deposits, and you pay rewards only for valid bugs.
- Managed Triage, so your engineers only see the reports that need their review. 99.3% of the reports our triage closed stayed closed after review.
- An audit competition before each upgrade or new market, so new code is reviewed before it holds deposits.
Your team keeps the decisions on scope, rewards, and which reports are valid.
We're at DAS, Stable Summit, and Breakpoint in London from 9 to 17 November. If you run a lending market, a CDP, or a vault, talk to us about a bug bounty on your live code.